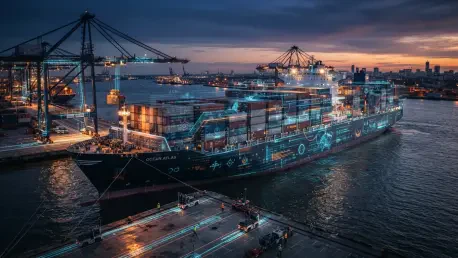
European and American regulators are introducing strict new mandates like the NIS2 Directive to force transportation companies to report cyber incidents within twenty-four hours. This move signifies a pivotal moment in the governance of global infrastructure, as the logistics industry transitions from a legacy of mechanical independence to a future of digital interdependence. For generations, the reliability of a cargo ship or a freight train was measured by the durability of its steel and the precision of its gears. However, the current landscape has been transformed by an aggressive wave of digitalization that connects every moving part of the supply chain to a centralized data network. This integration has unlocked immense efficiencies, but it has simultaneously exposed the world’s most critical shipping lanes and transit routes to vulnerabilities that were previously inconceivable. As the friction between physical operations and digital management increases, the industry must recognize that cybersecurity is no longer an optional IT expense but a fundamental pillar of operational safety and economic resilience.
The Shift: From Mechanical Reliability to Digital Complexity
The transition from purely mechanical systems to digitally integrated networks has redefined the operational baseline for transport providers. In the past, the industry relied on “air-gapped” systems that were physically isolated from the internet, making them inherently resistant to remote tampering. While these systems lacked the sophisticated tracking and optimization capabilities available today, they offered a level of predictable reliability that is increasingly difficult to maintain in a hyper-connected environment. The move toward automation and real-time data exchange has created a situation where the digital and physical realms are inextricably linked, meaning that a failure in one domain inevitably leads to a crisis in the other.
The Paradox: Modernized Logistics and Infrastructure Fragility
In previous decades, transport systems were often described as being “too dumb to fail” in a digital sense. Mechanical components were predictable, and failures were typically handled with physical tools and manual labor. This analog foundation provided a level of resilience against remote interference, as there were no invisible lines connecting a ship’s engine or a train’s braking system to the wider world. The shift to a smart infrastructure has traded this simplistic reliability for high-speed data exchange and automated oversight, which, while efficient, introduces a layer of complexity that is susceptible to sophisticated cyber manipulation.
The modern logistics landscape is now governed by GPS, satellite communications, and a vast network of IoT sensors. These technologies allow for unprecedented visibility into fleet locations and cargo conditions, yet they introduce software vulnerabilities that a mechanical wrench cannot fix. This shift represents a fundamental change in the nature of transport safety, where the very tools designed to enhance monitoring and efficiency can become the primary points of failure if compromised by a digital threat. The industry must now navigate the challenge of maintaining the speed of modern logistics without sacrificing the fundamental stability that analog systems once provided.
Systemic Risks: Automated Software and Operational Safety
The reliance on hyper-connected ecosystems has created a vulnerability where even routine updates can lead to catastrophic downtime across entire supply chains. Automated software deployments, intended to keep systems secure and functional, can inadvertently ground fleets or disable safety monitoring if the code contains errors or is tampered with by attackers during the distribution process. This devolving evolution highlights a growing fragility within the sector, where the complexity of the digital layer sometimes outweighs the robustness of the physical hardware it controls.
Furthermore, the integration of third-party software and cloud-based management platforms has expanded the attack surface far beyond the internal network of any single company. When a logistics provider utilizes an automated dispatch system or a remote vessel monitoring service, they are essentially importing the security posture of their vendors into their own operations. This interdependency means that a breach at a small software firm can have cascading effects, potentially halting the operations of major ports or international trucking fleets. Ensuring the integrity of these automated systems requires a rigorous approach to software supply chain security that was previously unnecessary in the era of manual logs and radio communications.
The Convergence: National Security and Cybercrime
The intersection of digital threats and physical transportation has elevated cybersecurity from a corporate concern to a matter of national security. As transport networks become more automated, they become attractive targets for both profit-driven criminals and state-sponsored actors seeking to exert geopolitical pressure. The ability to disrupt the flow of essential goods or disable public transit systems provides malicious entities with a level of leverage that was once only possible through physical sabotage. Consequently, the protection of transport data and control systems has become a critical requirement for maintaining the stability and safety of modern society.
The Challenge: Normalization of Deviance and Critical Infrastructure
A significant concern for industry experts is the concept of the normalization of deviance, where small technical anomalies are ignored until they lead to a major disaster. In the context of digital security, this often manifests as overlooked system capabilities or hidden backdoors within imported technology that are dismissed as minor bugs. A chilling example of this was the discovery of remote kill-switches in public transport vehicles that authorities were unaware of, posing a direct threat to public safety. When these deviations from standard safety protocols become accepted as the norm, the stage is set for a systemic failure that can be exploited by adversaries.
Addressing this deviance requires a cultural shift within transportation organizations to treat every digital anomaly with the same seriousness as a mechanical defect. National resilience depends on the ability of operators to identify and mitigate these hidden risks before they are activated by a malicious actor. This involves not only better monitoring technology but also a more skeptical approach to the procurement of hardware and software from regions where state interference is common. By identifying and closing these hidden gaps, the transport sector can reinforce its role as a stable backbone for national and international trade.
Criminal Synergy: The Rise of Cyber-Enabled Cargo Theft
There is an increasing synergy between digital hackers and traditional organized crime syndicates that has fundamentally changed the nature of cargo theft. This combined criminal enterprise uses data as a key to bypass physical locks and guards, targeting high-value shipments like retail goods and food supplies with surgical precision. By infiltrating the internal networks of logistics providers, criminals can identify the exact location and contents of containers, allowing them to coordinate physical heists based on stolen digital manifests and real-time tracking information.
This convergence of digital and physical crime means that cargo is often stolen before the carrier even realizes their network has been breached. Hackers might use spearphishing to gain access to a dispatcher’s credentials, which then allows them to redirect a shipment to a fraudulent location or disable the GPS tracking on a high-value trailer. This sophisticated approach reduces the risk for the criminals while increasing the financial and operational impact on the logistics firm. To combat this, security strategies must integrate digital monitoring with physical protection, recognizing that the safety of the goods is now entirely dependent on the security of the data that tracks them.
Global Regulatory Responses: Standards and Digital Sovereignty
In response to the escalating threat environment, governments around the world have begun to implement comprehensive regulations designed to standardize security across the transport sector. These mandates represent a departure from the voluntary guidelines of the past, as authorities recognize that the interconnected nature of modern logistics means that a single weak link can jeopardize the entire system. By establishing a baseline of required security practices, regulators hope to foster a more resilient global network that can withstand and recover from digital disruptions more effectively.
Legislative Mandates: Forcing Resilience Through Regulation
As the transport sector becomes a primary target, governments are moving away from optional guidelines toward mandatory security standards that carry significant penalties for non-compliance. In the European Union, the NIS2 Directive classifies transport as an essential sector, requiring strict incident reporting and vulnerability disclosure within narrow timeframes. Similarly, the United States has introduced the Cyber Incident Reporting for Critical Infrastructure Act, which mirrors the urgency of European laws by demanding rapid notification of significant cyber incidents and ransomware payments to federal authorities.
These regulations are designed to create a culture of transparency and accountability that has historically been lacking in the private logistics sector. By requiring companies to share information about attacks, regulators can identify broader trends and issue warnings to other operators before a local issue becomes a national crisis. This collective defense model is essential for protecting the complex, cross-border supply chains that define modern commerce. Organizations must now view compliance not as a bureaucratic burden, but as a necessary framework for maintaining the trust of their partners and the public.
Digital Sovereignty: Protecting the Vital Organs of Trade
Beyond simple reporting, new laws such as the Active Cyber Defense Law in Japan aim to protect the vital organs of national infrastructure from foreign interference. These regulations emphasize digital sovereignty, encouraging companies to be more transparent about their supply chains and the origin of their software and hardware. This move is intended to prevent the long-term integration of potentially compromised technology into critical transport networks, ensuring that the control systems for ports, rails, and aviation remain under the oversight of trusted authorities.
The push for digital sovereignty also involves a move toward localizing the management of critical data and ensuring that foreign entities cannot remotely access sensitive logistics information. This shift is particularly important as more transport assets become autonomous and rely on continuous data feeds for safe operation. By prioritizing the use of secure-by-design technology from vetted manufacturers, governments and private operators can reduce the risk of state-sponsored espionage and sabotage. This regulatory wave is a clear indication that the era of unmonitored digital expansion in the transport sector has ended, replaced by a more controlled and secure approach.
Strategic Frameworks: Building a Resilient Transport Network
To navigate this complex landscape, transportation organizations must adopt a holistic security framework that addresses both the digital and physical aspects of their operations. This requires a departure from traditional siloed thinking, where IT and physical security were treated as separate departments with distinct goals. In the modern era, these two disciplines must be integrated into a single, unified strategy that focuses on maintaining operational continuity in the face of diverse and evolving threats.
Asset Protection: Securing Mobile Endpoints and Moving Targets
In the logistics world, an endpoint is no longer just an office computer; it is a moving ship, a delivery truck, or a locomotive traversing vast geographic distances. Because these assets operate across thousands of miles and connect to various public and private networks, traditional perimeter security is entirely ineffective. Organizations must implement universal endpoint security that protects these mobile assets as they move through different environments, ensuring that the security perimeter follows the asset rather than remaining fixed at a central office.
This proactive approach involves deploying advanced monitoring tools directly onto the vehicles and vessels themselves, allowing for the detection of anomalies in real-time. For instance, an unexpected change in a locomotive’s braking system software or an unauthorized data transfer from a ship’s navigation console can be flagged and mitigated before it results in a physical accident. By treating every transport asset as a critical digital node, companies can provide constant protection regardless of location, ensuring that the mobility of the fleet does not become a security liability.
Procurement Integrity: The Role of Secure-by-Design Principles
When investing in new fleets or management software, transportation companies must prioritize secure-by-design principles over the pursuit of the lowest price tag. This involves purchasing from trusted manufacturers who adhere to strict transparency standards and provide clear documentation regarding the security of their hardware and software components. Strategic procurement ensures that the technology powering the future of transport is built with a foundation of integrity, rather than serving as a backdoor for potential attackers.
Furthermore, companies should demand long-term support and regular security patches as part of their procurement contracts. The long lifecycle of transport assets—often spanning decades—means that a ship or truck purchased today must remain secure against threats that do not yet exist. By choosing partners who demonstrate a commitment to ongoing security maintenance, logistics providers can avoid the trap of operating legacy systems that are too old to patch but too expensive to replace. This forward-looking approach to investment is vital for building a transport network that remains resilient over the long term.
Collaborative Defense: Ending the Culture of Silence
The transport industry has historically been hesitant to share information about security breaches due to concerns about brand reputation and competitive disadvantage. However, for the sector to stay ahead of sophisticated threats, this culture of silence must end in favor of a collaborative defense model. Transparent reporting to organizations like Europol or the Cybersecurity and Infrastructure Security Agency allows for a coordinated global response to emerging threats, turning local lessons into global defenses.
By sharing anonymized data about attack vectors and successful mitigations, transport providers can help each other strengthen their collective posture. This collaborative spirit is already visible in some maritime and aviation information-sharing centers, where competitors work together to identify common adversaries. When the industry speaks with one voice and acts in a coordinated manner, it becomes a much harder target for both petty criminals and state-aligned groups. This shift toward transparency is the final piece of the puzzle in creating a global transport network that is as secure as it is efficient.
Actionable Steps for Future Logistics Stability
The transportation sector successfully integrated digital tools to enhance global trade, but this progress came with an urgent need for revised safety protocols. Organizations that prioritized IT hygiene and endpoint protection early on were able to mitigate the most severe impacts of the cyber-enabled cargo theft wave. By adopting a secure-by-design philosophy, many leading carriers reduced their reliance on vulnerable legacy systems, thereby closing the gap that hackers had previously exploited. These proactive measures established a new industry standard where digital integrity was viewed as being just as critical as mechanical maintenance.
Moving forward, the industry should focus on deepening its cooperation with national security agencies to identify hidden vulnerabilities in the global supply chain. Logistics providers must continue to invest in automated monitoring and incident response tools that can operate in the disconnected environments common in maritime and long-haul trucking. Furthermore, a renewed emphasis on employee training is necessary to prevent social engineering attacks from serving as the initial entry point for more destructive breaches. By maintaining this rigorous commitment to digital and physical security, the transport industry can ensure that the global economy continues to move forward safely and reliably.